
OT Security Assessment
“Where do we actually stand, and what could really break the process?”
- 1.1OT Security Posture Assessment against all seven IEC 62443 Foundational Requirements
- 1.2ThePlantWalk
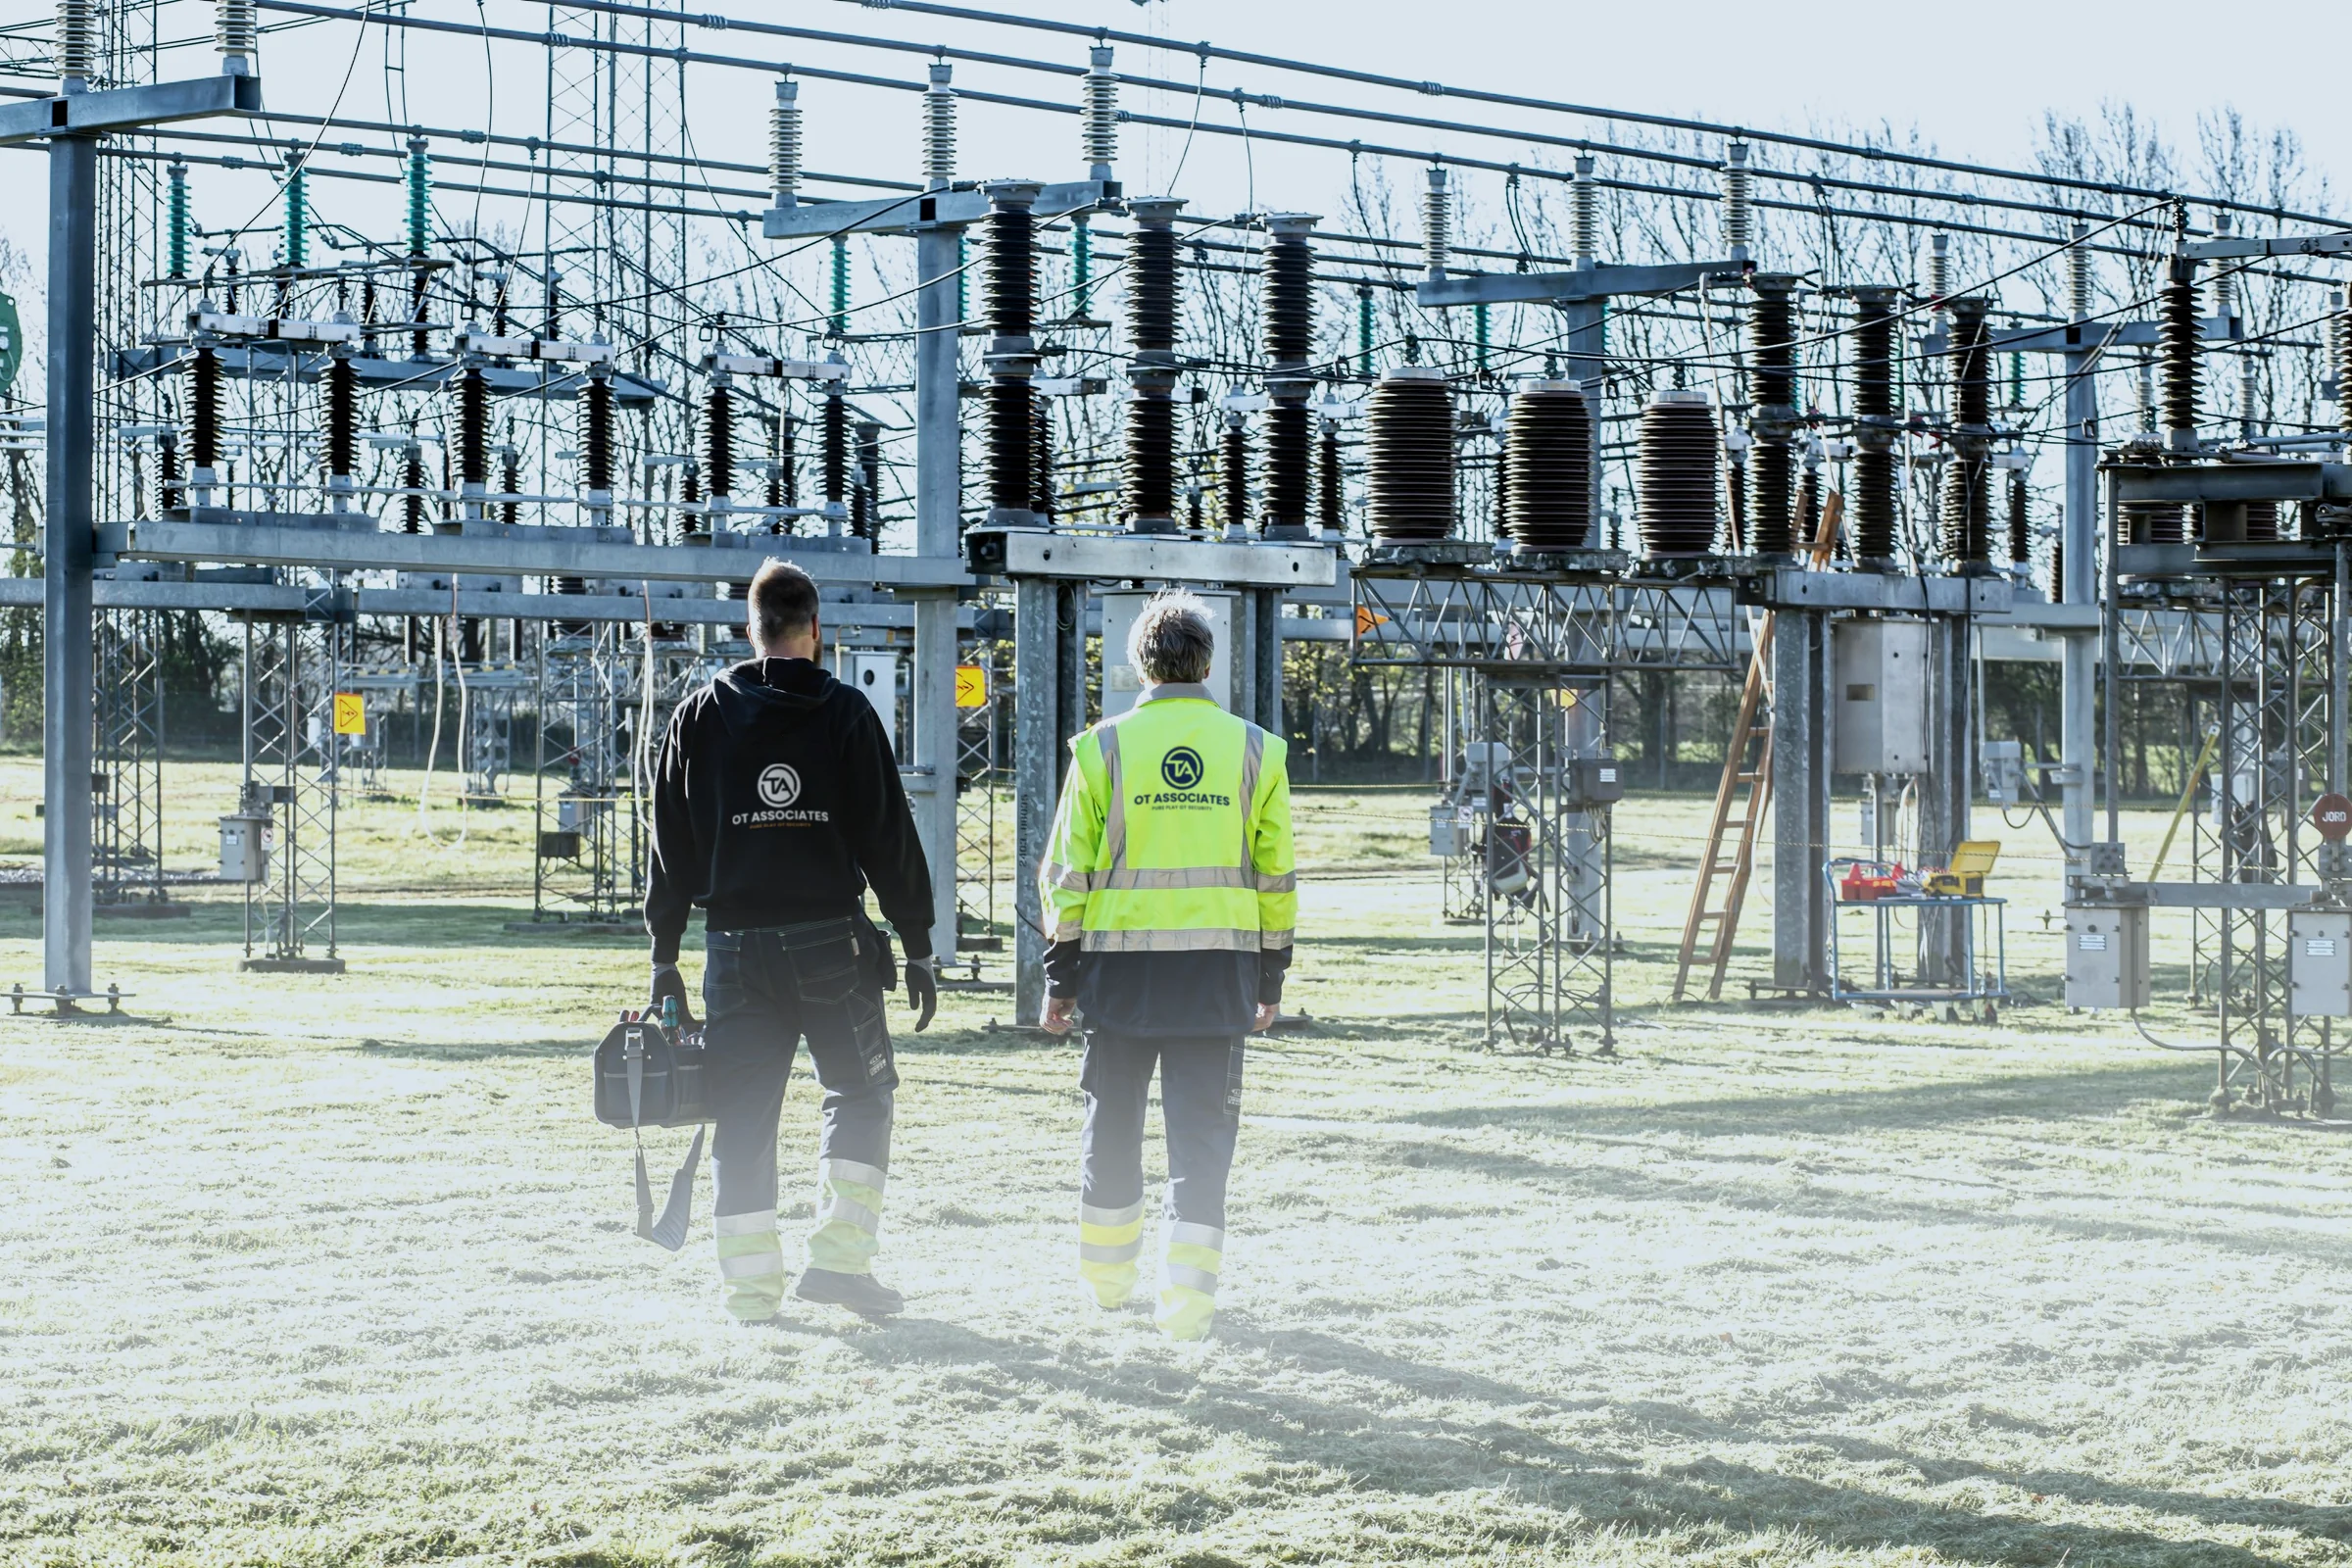
On-site security walkdown, asset by asset, by senior practitioners
- 1.3OT Asset Inventory and Network Visibility
A complete, living map of assets and flows
- 1.4OT Cyber Risk Assessment
Zones, conduits and target security levels per IEC 62443-3-2
- 1.5OT Penetration Testing on non-production and representative systems, never the live process
- 1.6OT Security Due Diligence for mergers and acquisitions
- Assets
- Compliance
- Risk
- Governance
- Deviations
Architecture & Engineering
“What should the defensible plant look like, by design?”
- 2.1OT Network Architecture and Segmentation Design
Zones, conduits and the industrial DMZ
- 2.2Isolated domains independent of corporate Active Directory, with secure remote access patterns
- 2.3Safety Instrumented System Security
IEC 62443 and IEC 61511 converged, so no cyber event can defeat a safety function
- 2.4Secure by Design for Capital Projects
Security embedded from FEED through commissioning
- 2.5Phased migration plans that protect availability at every step
- Assets
- Risk
- Governance
- BCM
Governance, Risk & Compliance
“How do we run security as a discipline that survives audits and staff turnover?”
- 3.1OT Cybersecurity Governance aligned to IEC 62443-2-1, with Micro Governance
Control ownership down to the individual asset
- 3.2OT Security Strategy, Roadmap and Investment Case the board can endorse
- 3.3OT Policies, Standards and Procedures tailored to plant reality
- 3.4Regulatory Compliance and Certification Readiness
IEC 62443, NCA OTCC, NCA ECC, NIS2, ADHICS, NESA and NERC CIP, with one control satisfying many frameworks
- Governance
- Users
- Compliance
- Assets
- Mitigation
- Risk
Implementation & Hardening
“How do we make the design real without ever risking the process?”
- 4.1Network Segmentation Implementation
Every change validated, tested and reversible, with operations holding the final word
- 4.2Secure Configuration and System Hardening
Baselines and golden images per asset class
- 4.3OT Identity, Access and Secure Remote Access on least privilege, brokered and monitored
- 4.4OT Vulnerability and Patch Management prioritised by process impact, not raw CVE score, with compensating controls where patching is not feasible
- Assets
- TPRM
- Users
- Compliance
- Deviations
- Mitigation
Monitoring & Response
“Can we see what is coming, and are we rehearsed to act?”
- 5.1OT Threat Detection and Continuous Monitoring by named senior OT engineers, around the clock
- 5.2Tool agnostic across Dragos, Claroty, Nozomi, Tenable OT and Microsoft Defender for IoT
- 5.3OT Incident Response Planning and Exercises
Playbooks, safe state procedures, tabletop and technical simulations
- 5.4OT Threat Intelligence and Advisories written for your sector and region, in a language a board can act on
- Assets
- Users
- Compliance
- Mitigation
Managed Services & Training
“How does this endure beyond a project, and who runs it with us?”
- 6.1OT Security Training and Competency Development
Role-based, field-assessed, in English, Arabic and Urdu
- 6.2Third Party and Supply Chain Security Assurance per IEC 62443-2-4, 4-1 and 4-2
- 6.3Virtual OT CISO and Retained Advisory
One named senior practitioner, permanently accountable
- 6.4Managed OT Governance and Compliance
Your programme run for you inside OTMATIX, your authority retained
- Deviations
- BCM
- Governance
One partner. Three ways to run it.
The whole journey under one multi-year agreement, one governance cadence and one evidence trail in OTMATIX. Authority and approvals always stay with you. Pick the model that fits.
Senior practitioners run the programme with you inside OTMATIX, anchored by a Virtual OT CISO. You retain authority and approval rights; the programme never stalls when your team is stretched.
Let’s secure every layer of your plant.
Begin with an OT Security Posture Assessment and ThePlantWalk. An evidenced view of your OT risk, and a clear path to the level of security you choose to hold.